Innovating Your Digital Future
Secure, scalable, and intelligent IT solutions engineered for modern enterprises.
Trusted by Modern Enterprises & Public Institutions
Delivering confidential engineering solutions across regulated industries.
15+ Offensive & Defensive Certifications
Our principal engineers hold elite credentials across offensive security, cloud architecture, and ISO standards.
Offensive Security Certified Professional
Certified Red Team Professional
Certified Red Team Analyst
Web Penetration Tester eXtreme
Mobile Application Penetration Tester
Certified Mobile Pentester — Android
Certified Mobile Pentester — iOS
Junior Penetration Tester
Information Security Management System
Certified Ethical Hacker
Ethical Hacking Essentials
Certified AppSec Practitioner
Certified Network Defender
Certified Network Security Professional
API Red Team Analyst
Web Red Team Analyst
Institutional Auditing & Compliance Matrix
Full-Spectrum Technology Engineering
Enterprise solutions aligned with Indonesian national standard KBLI registrations and global security standards.
Artificial Intelligence Programming
Building custom Large Language Models, agentic workflows, and intelligent automation pipelines.
Information Security Consulting
Institutional penetration testing, red teaming, asset protection, and structural security auditing.
Custom Software Engineering
Distributed backend architecture, bespoke software suites, and high-concurrency business logic.
Digital Identity Provisioning
Secure identity infrastructures, multi-factor verification systems, and digital trust layers.
Hardware Integration & Embedded Systems
Hardware-software integration, telemetry acquisition platforms, and resilient embedded controllers.
Sovereign Infrastructure Operations
Mission-critical server architecture, bare-metal orchestration, and containerized cloud operations.
High-Throughput Database Architecture
Distributed database architecture, real-time replication pipelines, and analytics clustering.
Enterprise Systems Architecture
Institutional systems design, microservice migration, and fault-tolerant service meshes.
Two Platforms. One Ecosystem.
Unified LLM API
at Wholesale Rates
$0.11 per $1 Credit
Stop paying retail price for LLM tokens. Route Claude 3.5 Sonnet, GPT-4o, DeepSeek R1, Grok 2, and 30+ frontier models through one drop-in OpenAI compatible API endpoint with institutional SLA.
Primevora Autonomous Agent Core
Experience our multi-agent orchestration architecture in action. Select an enterprise scenario to observe real-time agent coordination, deterministic state machines, and zero-trust validation.
High-Stakes Architecture In Production
Real-world institutional deployments delivering uncompromising security and high throughput.
Vulnerability Assessment
Continuous automated scanner noise floods engineering backlogs with raw, unverified CVE alerts lacking business context, verified exploitability, or clear SLA prioritization.
A recurring quarterly cycle of asset discovery, authenticated vulnerability scanning, and manual false-positive triage, mapping findings to CVSS 4.0 severity rankings and guaranteed patch SLAs.
Enumerate external and internal assets, shadow IT, and exposed services to establish an authoritative scope baseline.
Credentialed and uncredentialed scans across host nodes, containers, and web applications using industry-standard scanner stacks.
Manual offensive validation of every automated scanner finding, eliminating false positives before reaching the risk register.
Confirmed findings ranked by CVSS 4.0 severity and business exposure, mapped directly to actionable SLA remediation tiers.
Penetration Testing & VAPT
Bank BTN handles highly sensitive financial records and transactions. Sophisticated threat actors target critical API layers, web/mobile app logic, and core banking infrastructure.
Full-Spectrum Hybrid VAPT employing automated and manual offensive audits (Blackbox, Greybox, Whitebox) split into Offensive Red Team exploit testing and Defensive Blue Team SOC threat mitigation.
Scan and exploit target endpoints using OWASP-aligned techniques including authorization bypass, race conditions, and business logic flaws.
Static and dynamic analysis of application sessions, rooted device local storage checks, cryptographic flaws, and reverse engineering obfuscation.
Domain scans, port enumeration, SSL/TLS configuration weaknesses, and outdated services verification on core banking hosts.
NIST SP 800-115 and OWASP framework alignment, regulatory validation, executive risk reporting, and re-test verification.
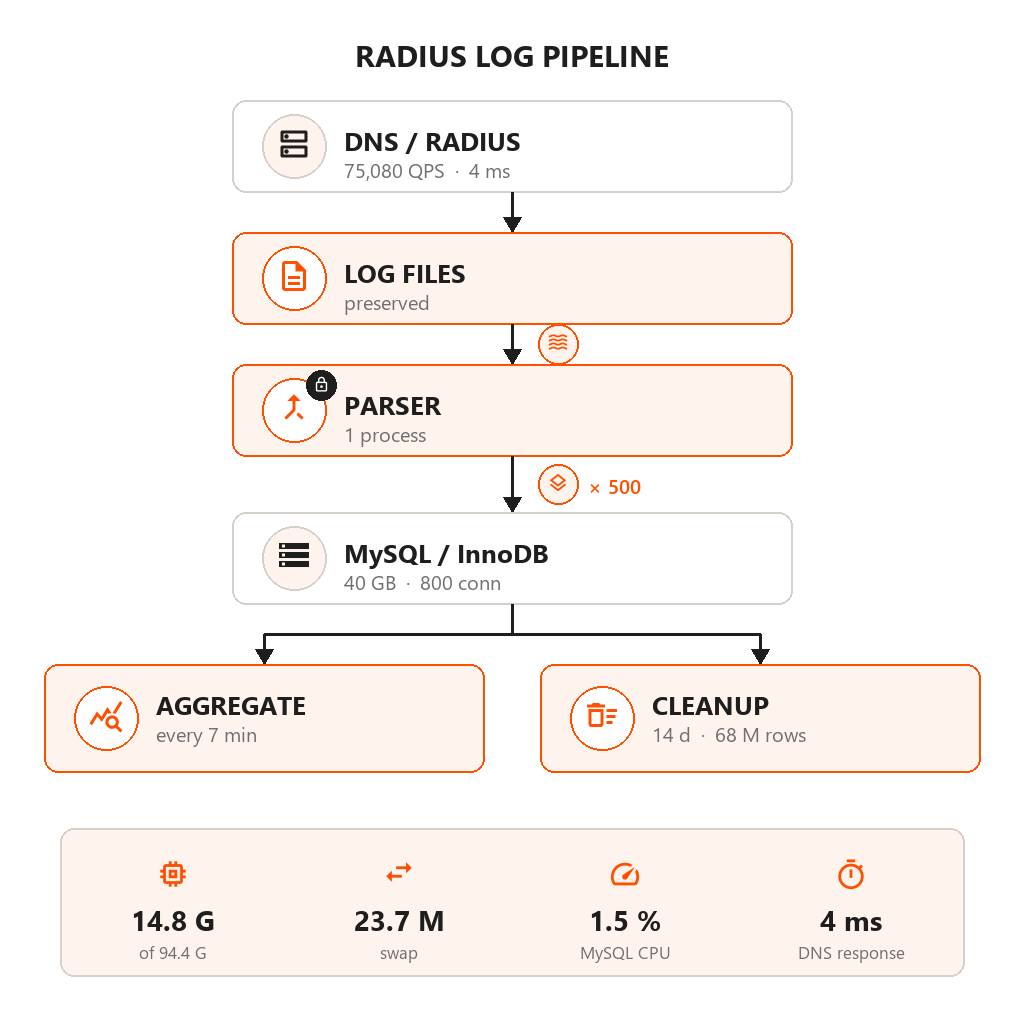
High-Volume RADIUS & DNS Optimization
Scaling high-volume mobile telecom billing systems. Production database suffered lock contention and memory exhaustion under 15,000+ requests per second during peak mobile traffic.
Re-engineered data pipelines with single flock-protected log parsers, fgets() stream reading, batched 500-row inserts, and hardened DNSSEC/ACL controls sustaining 75,000 queries per second.
Collapsed ten overlapping log parsers into one flock-protected process, eliminating duplicate reads and lock contention.
Replaced full-file fread() loads with fgets() streaming, holding pipeline memory usage at 14.8 GB of 94.4 GB RAM without swap exhaustion.
One INSERT per log line became 500-row batches on a 14-day retention cycle with nightly cleanup, holding MySQL CPU at 1.5%.
Resilient DNS configurations with DNSSEC, precise ACL controls, and structural mitigation against DDoS amplification up to 75,000 QPS.
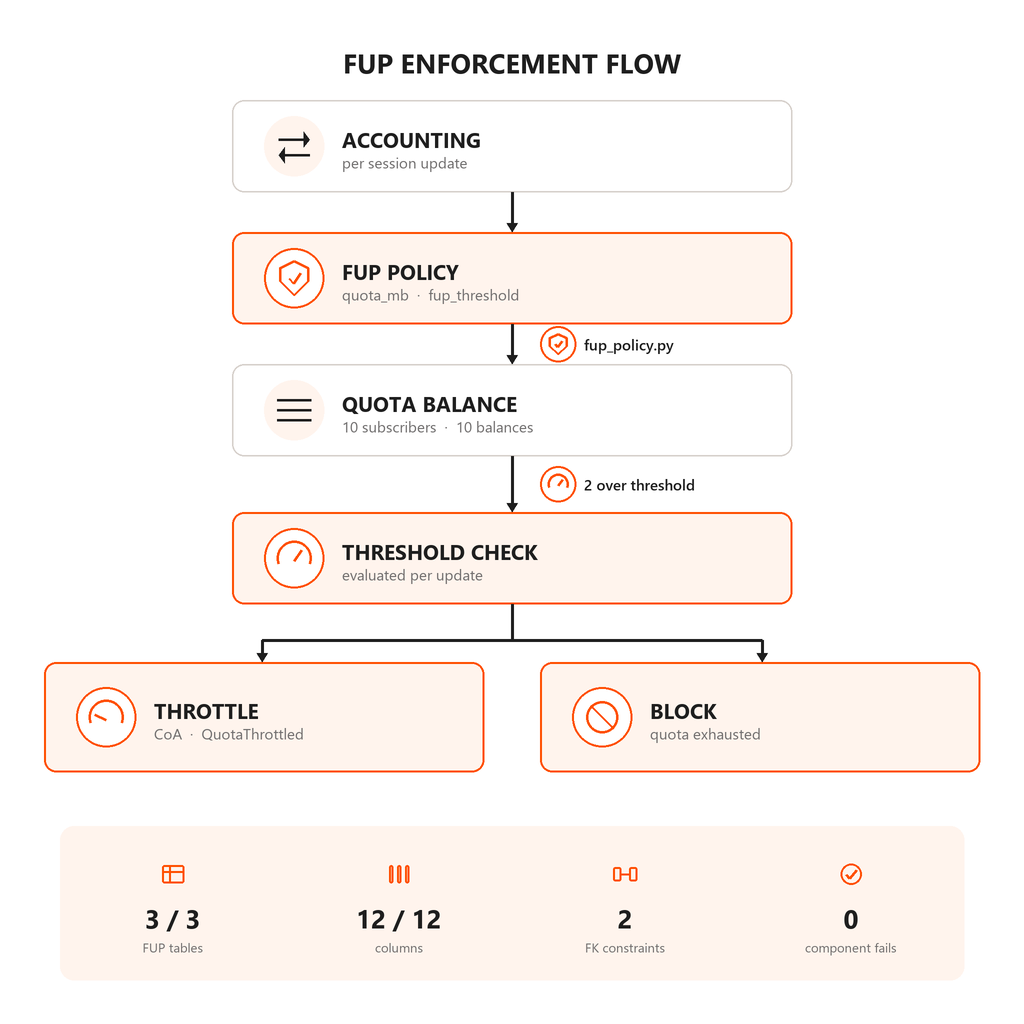
Fair Usage Policy (FUP) & Billing Automation
Carrier needed automated Fair Usage Policy (FUP) threshold enforcement integrated directly into their live FreeRADIUS AAA stack without interrupting active subscriber data sessions.
Engineered FreeRADIUS python3 policy module evaluating quota balances against each accounting update and issuing RADIUS CoA (Change of Authorization) requests to throttle bandwidth dynamically.
fup_policy.py running under the FreeRADIUS python3 module, evaluating quota_mb and fup_threshold against each accounting update.
Three synchronized tables (fup_policy, subscribers, quota_balance) carrying twelve core columns and foreign key constraints.
coa_trigger.sh issuing CoA-Requests with Cisco-AVPair QuotaThrottled-IN/OUT, moving sessions onto throttled QoS without dropping users.
Automated dual-host verification pass: zero missing tables, zero missing columns, and FUP_ENABLED validation across all carrier nodes.
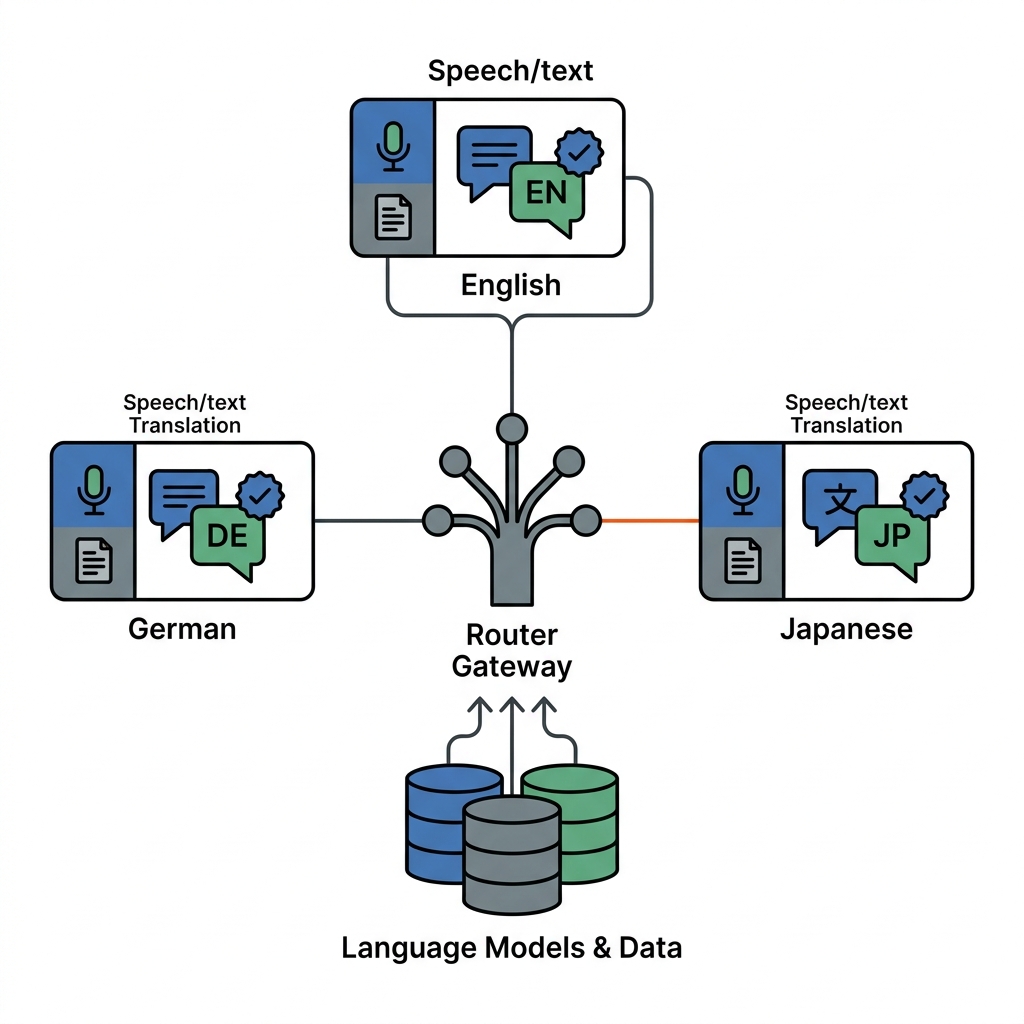
Agentic AI: Sprechengate
IELTS, TOEFL, Goethe, and JLPT exam mock scoring was bottlenecked by manual human evaluation ($25/test) with a 72-hour turnaround time and severe grading inconsistency.
A Multi-Agent Predictor Network (MAPN) that ingests speaking and writing payloads, normalizes international accents, cross-audits rubrics, and generates custom study plans instantly.
Ingests speaking audio and essay payloads, normalizes regional accents, and routes packages to specialized linguistic agents.
Anglo-Metrics (fluency & lexical depth), Teutonic-CEFR (German morphology), and Kanji-Syntax (JLPT context) score content.
Cross-checks evaluation scores recursively against verified official examiner rubrics to prevent hallucinations.
Growth agents analyze sectional breakdowns to generate customized lesson roadmaps and pinpoint remediation exercises.
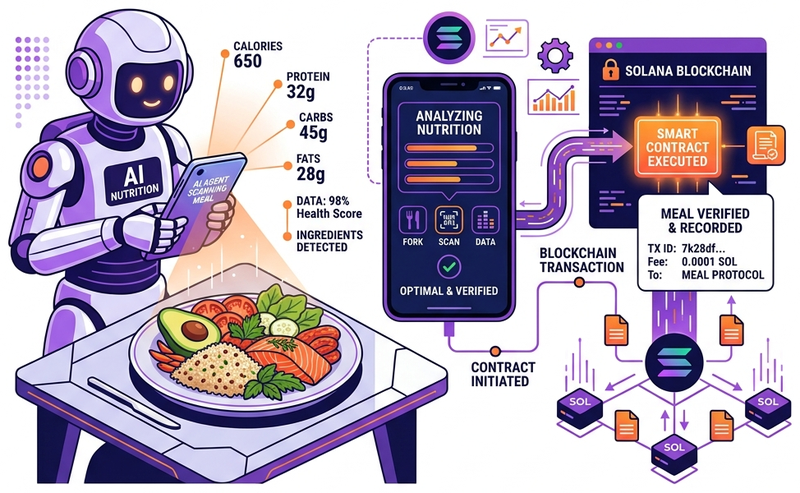
Yunabite — Agentic Web3 Extension
While DePIN protocols successfully tokenize movement, nutrition tracking remains manual and prone to falsification. Users lack verifiable, on-chain HealthFi rewards automation.
Connecting Web2 AI computer-vision scanning to Solana via the Solana Agent Kit. Yunabite autonomous agent parses meal macros and executes on-chain ledger actions, cNFT minting, and escrow settlement.
Ingests smartphone camera photos to extract macronutrients, calorie densities, and food groups automatically.
Autonomous LLM-driven agent connecting Web2 vision models directly to Solana smart contracts.
Mints and airdrops compressed NFTs (cNFTs) on Solana for verified healthy habit streaks with minimal gas fees.
Smart contract locking USDC where the Yunabite Agent acts as an objective arbiter releasing rewards or executing penalty slashes.
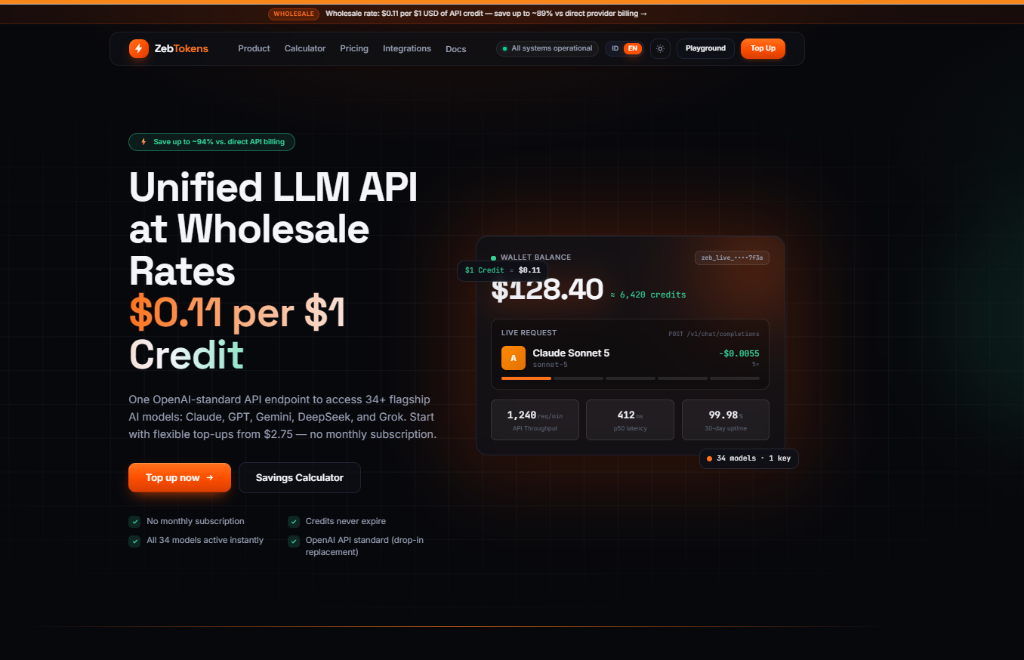
ZebTokens — Wholesale LLM API Gateway
Developers and enterprise AI agents face exorbitant retail token markups, fragmented vendor billing (OpenAI, Anthropic, Google, xAI), and rate limits that throttle high-throughput production workloads.
A unified OpenAI-standard proxy gateway routing requests across 34+ flagship models at wholesale rates ($0.11 per $1 credit) with zero monthly subscription commitments, credits that never expire, and sub-millisecond billing.
Pre-purchased institutional token volumes pass up to ~89%–94% cost savings directly to builders with flexible top-ups starting at $2.75.
Access Claude Sonnet 5, GPT-4o, DeepSeek V3, Gemini 2.0, and Grok 2 through a single drop-in OpenAI-compatible endpoint.
Zero-buffering reverse proxy architecture sustaining 1,248+ req/min with a median p50 latency of 412ms and 99.98% 30-day uptime.
Swap base_url and api_key in existing codebases with zero refactoring. Native streaming, tool calling, and structured outputs supported.
Rigorous 5-Stage Engineering Lifecycle
From threat-modeled architectural discovery to post-launch sovereign support.
Empathize & Discover
Deep stakeholder interviews, technical debt audits, and architectural threat profiling.
Define & Specify
Detailed systems specifications, schema contracts, throughput targets, and compliance mapping.
Ideate & Architect
Fault-tolerant topologies, zero-trust boundary designs, and database replication schemes.
Prototype & Harden
Iterative sprints with automated CI/CD security scanning, code reviews, and penetration testing.
Test & Sovereign Launch
Staged canary rollouts, full source code and IP handover, and 1-Year ATS maintenance initiation.
Vision & Mission
What we are building toward, and the commitments we hold ourselves to on the way there.
“To be the technology partner institutions worldwide trust with the systems they cannot afford to lose.”
Security by Design
Engineer security in from the first architectural decision — threat modeling, zero-trust boundaries, and regulatory compliance, rather than an audit bolted on at the end.
Built for Future Load
Build for the load that is coming, so systems absorb explosive data growth and real-time computation without performance regression.
100% IP & Code Handover
Hand over everything we build: source code, deployment scripts, and architecture documentation transfer in full, with no recurring licensing.
Post-Launch Accountability
Stay accountable after launch, with a standard one-year technical support (ATS) guarantee covering patch management and incident response.
Strategic Core Values
Engineering resilient architectures that withstand adversarial threats while delivering rapid, verifiable business momentum.
Institutional Security
Built upon rigorous threat modeling, proactive information security compliance, and zero-trust infrastructure paradigms.
High-Throughput Scalability
Systems engineered to handle explosive data writes and real-time computation without performance regression.
Absolute Transparency
Clear milestone timelines, comprehensive architectural documentation, and open transfer of source code.
Frequently Asked Questions
Clear answers regarding licensing, intellectual property, security guarantees, and project execution.
Have a Custom Engagement?
Direct dialogue with principal architects.
We sign strict bilateral NDAs prior to any technical architecture or security scope review.
Chat with Principal Engineer→100% of custom source code, documentation, infrastructure scripts, and deployment artifacts are transferred entirely to your organization upon project completion. We do not retain proprietary lock-in or recurring IP licensing fees.
Primevora provides 365 days of comprehensive technical maintenance post-launch. This covers zero-day patch deployments, configuration adjustments, performance monitoring, and guaranteed incident SLA response.
All infrastructure and deployments strictly comply with Indonesian data privacy laws (UU PDP), Bank Indonesia / OJK regulatory frameworks, and Tier-3 domestic datacenter residency mandates.
Yes. ZebTokens provides a 100% drop-in replacement for OpenAI API endpoints with 34+ models, while ZebPod delivers automated bare-metal KVM VPS and dedicated GPU compute with sovereign interconnects.
Initiate Your Technical Consultation
Direct access to principal systems architects and offensive security engineers.
Direct WhatsApp Dispatch
Direct line with senior engineering leads for immediate scope inquiries, emergency VAPT, or project kickoffs.
Formal Procurement & Security
Send RFPs, compliance questionnaires, or bilateral NDA drafts directly to our security operations mailbox.