
High-Stakes Architecture in Production
Real-world institutional deployments delivering uncompromising security and high throughput.
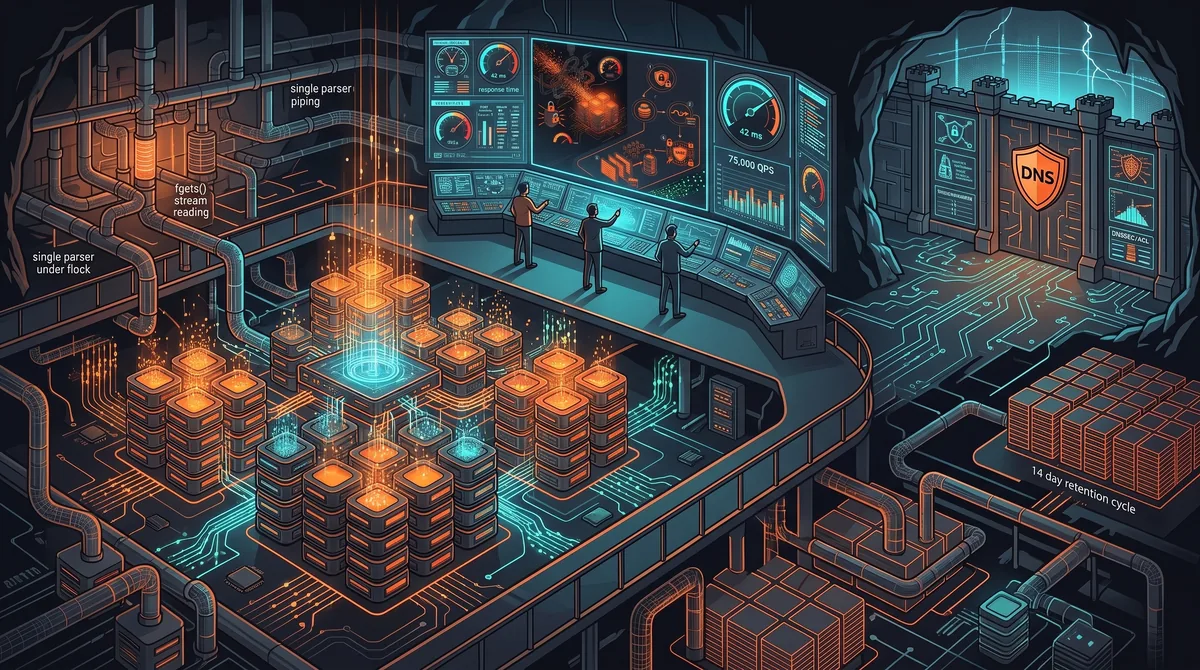
RADIUS & DNS Scaling
Scaling high-volume mobile telecom billing systems. Production database suffered lock contention and memory exhaustion under 15,000+ requests per second during peak mobile traffic.
Re-engineered data pipelines with single flock-protected log parsers, fgets() stream reading, batched 500-row inserts, and hardened DNSSEC/ACL controls sustaining 75,000 queries per second.
Collapsed ten overlapping log parsers into one flock-protected process, eliminating duplicate reads and lock contention.
Replaced full-file fread() loads with fgets() streaming, holding pipeline memory usage at 14.8 GB of 94.4 GB RAM without swap exhaustion.
One INSERT per log line became 500-row batches on a 14-day retention cycle with nightly cleanup, holding MySQL CPU at 1.5%.
Resilient DNS configurations with DNSSEC, precise ACL controls, and structural mitigation against DDoS amplification up to 75,000 QPS.
Full-Spectrum Penetration Test
Financial institutions process highly sensitive customer data and transactions. Attackers actively probe exposed APIs, web and mobile application logic, and core infrastructure for exploitable weaknesses before defenders find them.
Full-Spectrum Hybrid VAPT employing automated and manual offensive audits (Blackbox, Greybox, Whitebox) to identify, validate, and prioritize exploitable vulnerabilities, followed by remediation guidance and re-testing.
Scan and exploit target endpoints using OWASP-aligned techniques including authorization bypass, race conditions, and business logic flaws.
Static and dynamic analysis of application sessions, rooted device local storage checks, cryptographic flaws, and reverse engineering obfuscation.
Domain scans, port enumeration, SSL/TLS configuration weaknesses, and outdated services verification on core banking hosts.
NIST SP 800-115 and OWASP framework alignment, regulatory validation, executive risk reporting, and re-test verification.
Quarterly Vulnerability Management
Continuous automated scanner noise floods engineering backlogs with raw, unverified CVE alerts lacking business context, verified exploitability, or clear SLA prioritization.
A recurring quarterly cycle of asset discovery, authenticated vulnerability scanning, and manual false-positive triage, mapping findings to CVSS 4.0 severity rankings and guaranteed patch SLAs.
Enumerate external and internal assets, shadow IT, and exposed services to establish an authoritative scope baseline.
Credentialed and uncredentialed scans across host nodes, containers, and web applications using industry-standard scanner stacks.
Manual offensive validation of every automated scanner finding, eliminating false positives before reaching the risk register.
Confirmed findings ranked by CVSS 4.0 severity and business exposure, mapped directly to actionable SLA remediation tiers.
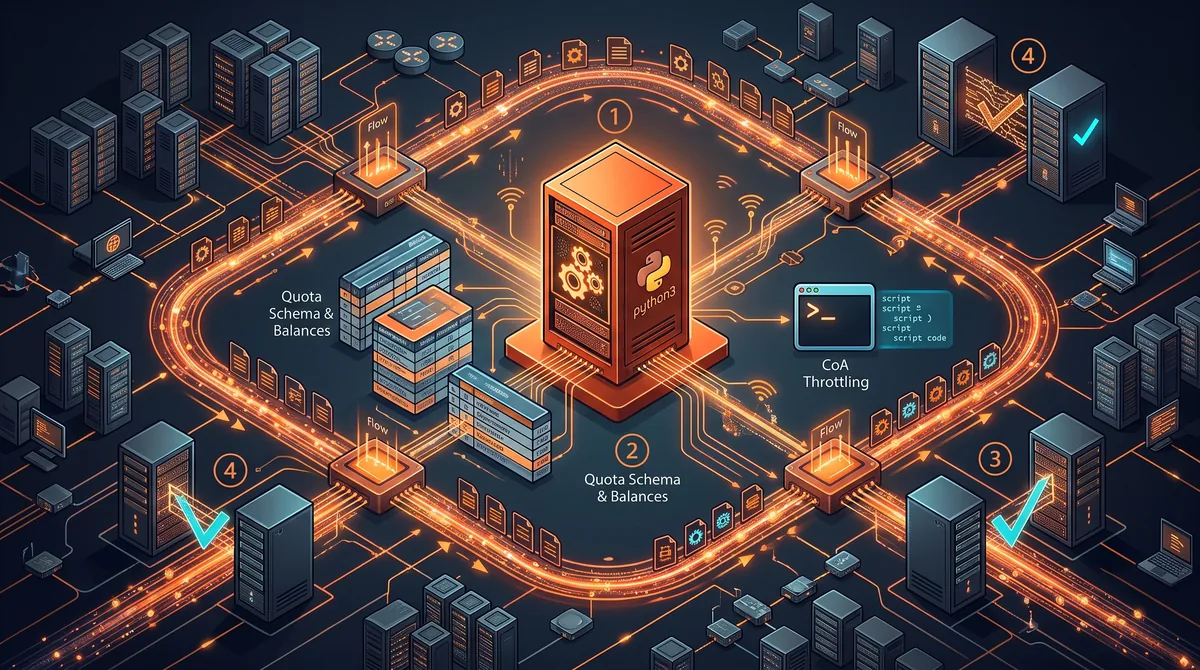
Fair Usage Policy Automation
Carrier needed automated Fair Usage Policy (FUP) threshold enforcement integrated directly into their live FreeRADIUS AAA stack without interrupting active subscriber data sessions.
Engineered FreeRADIUS python3 policy module evaluating quota balances against each accounting update and issuing RADIUS CoA (Change of Authorization) requests to throttle bandwidth dynamically.
fup_policy.py running under the FreeRADIUS python3 module, evaluating quota_mb and fup_threshold against each accounting update.
Three synchronized tables (fup_policy, subscribers, quota_balance) carrying twelve core columns and foreign key constraints.
coa_trigger.sh issuing CoA-Requests with Cisco-AVPair QuotaThrottled-IN/OUT, moving sessions onto throttled QoS without dropping users.
Automated dual-host verification pass: zero missing tables, zero missing columns, and FUP_ENABLED validation across all carrier nodes.
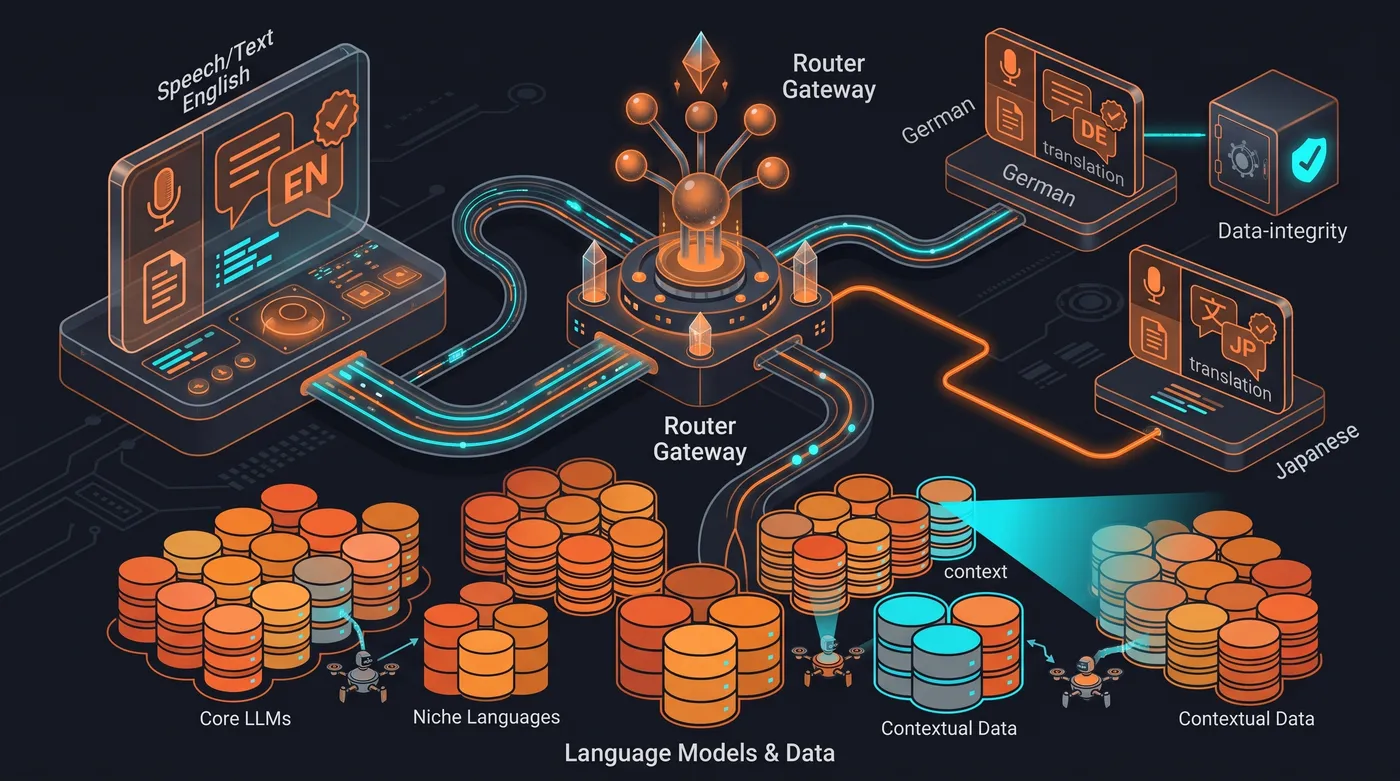
AI Language Exam Grading
IELTS, TOEFL, Goethe, and JLPT exam mock scoring was bottlenecked by manual human evaluation ($25/test) with a 72-hour turnaround time and severe grading inconsistency.
A Multi-Agent Predictor Network (MAPN) that ingests speaking and writing payloads, normalizes international accents, cross-audits rubrics, and generates custom study plans instantly.
Ingests speaking audio and essay payloads, normalizes regional accents, and routes packages to specialized linguistic agents.
Anglo-Metrics (fluency & lexical depth), Teutonic-CEFR (German morphology), and Kanji-Syntax (JLPT context) score content.
Cross-checks evaluation scores recursively against verified official examiner rubrics to prevent hallucinations.
Growth agents analyze sectional breakdowns to generate customized lesson roadmaps and pinpoint remediation exercises.
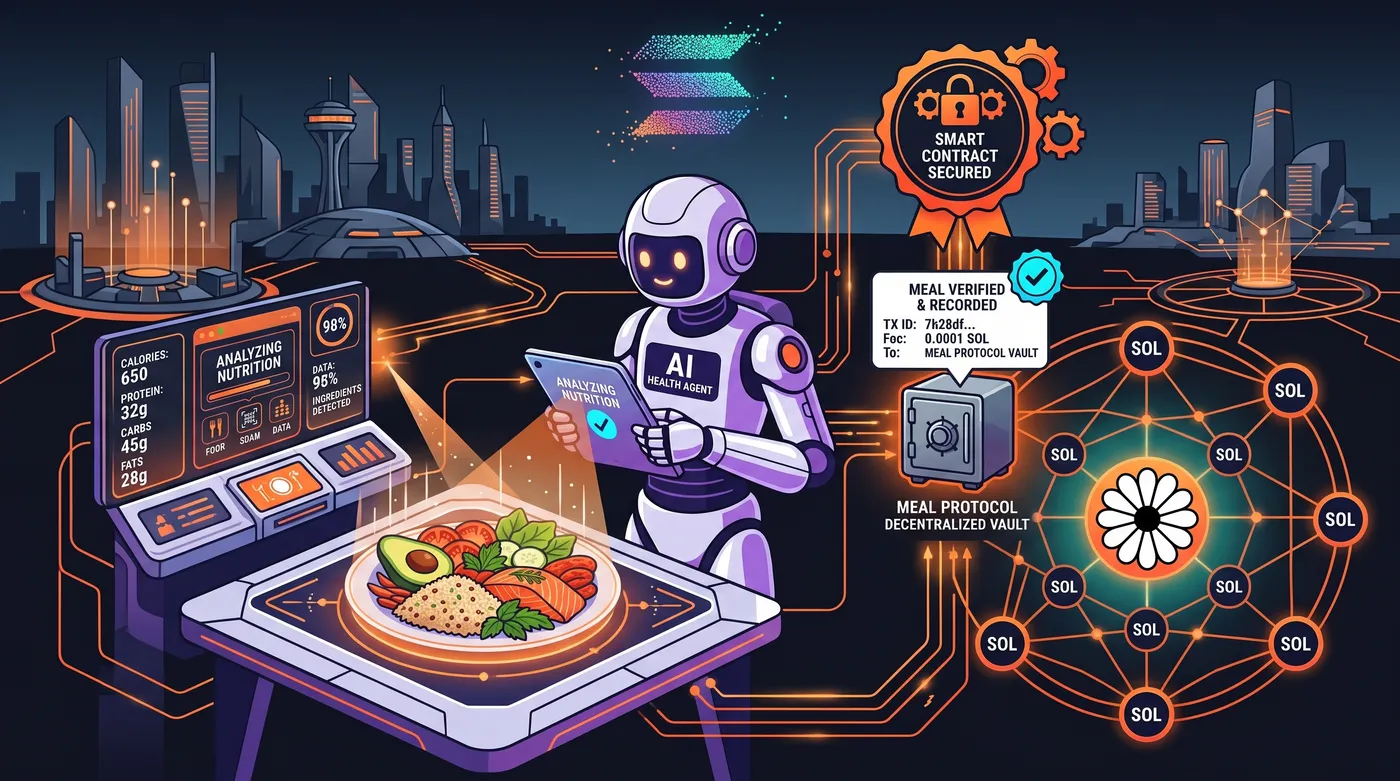
AI Nutrition Tracking
While DePIN protocols successfully tokenize movement, nutrition tracking remains manual and prone to falsification. Users lack verifiable, on-chain HealthFi rewards automation.
Connecting Web2 AI computer-vision scanning to Solana via the Solana Agent Kit. Yunabite autonomous agent parses meal macros and executes on-chain ledger actions, cNFT minting, and escrow settlement.
Ingests smartphone camera photos to extract macronutrients, calorie densities, and food groups automatically.
Autonomous LLM-driven agent connecting Web2 vision models directly to Solana smart contracts.
Mints and airdrops compressed NFTs (cNFTs) on Solana for verified healthy habit streaks with minimal gas fees.
Smart contract locking USDC where the Yunabite Agent acts as an objective arbiter releasing rewards or executing penalty slashes.
Facing a similar challenge? Walk through the architecture with our engineers.
Book a Consultation